
Deploy in under 60 minutes with zero downtime or operational risk
AuthFore CyberSecurity Accountant - Zero Trust Security through Cyber-Fiscal Engineering, passively transforms raw infrastructure log exhaust into a unified, multi-protocol behavioral risk score—instantly flagging directory reconnaissance, ransomware mutation spikes, and insider session anomalies on an executive dashboard.
Enterprise Security Use Cases
| Use Case / Example |
|---|
| Detecting BloodHound & LDAP Reconnaissance An attacker breaches an endpoint and launches an automated LDAP enumeration tool. Rather than blocking blindly, ldapmonitor flags an abnormal score surge (42.5 vs baseline 3.1) alerting the SOC in real time. 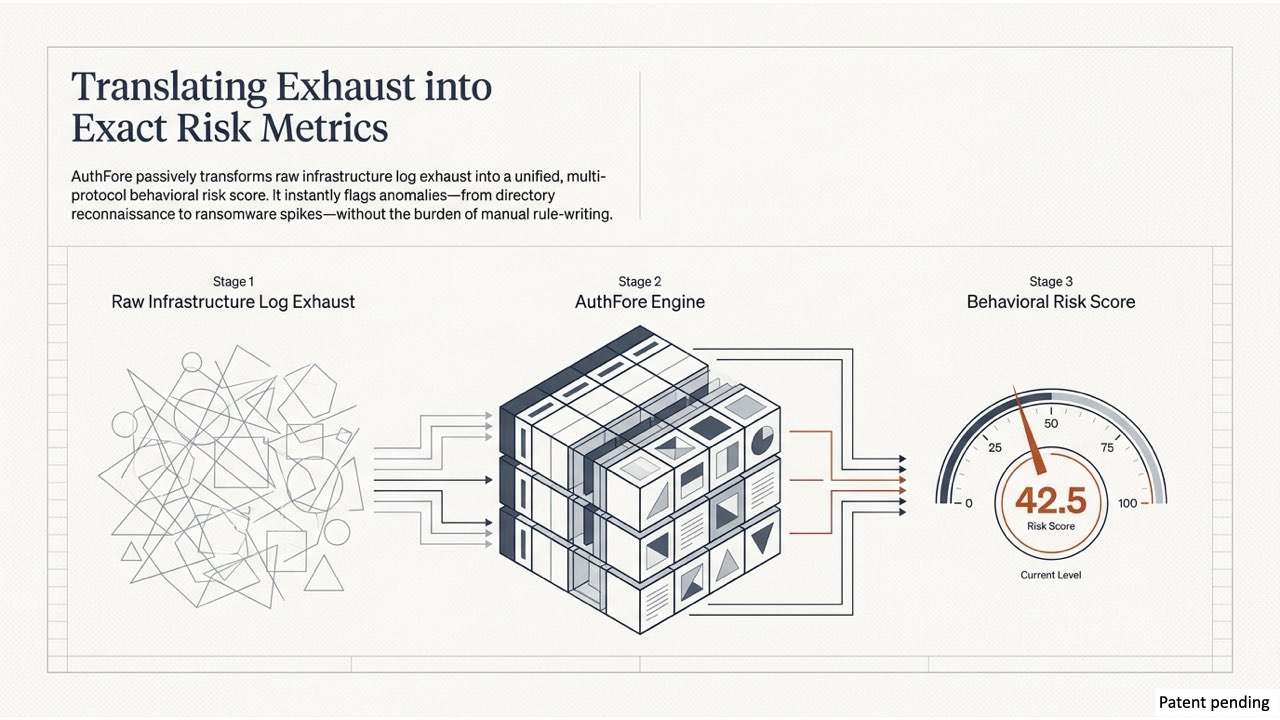 |
| Ransomware vs. Nightly Backup Discrimination While a nightly backup script reads files, ransomware modifying extensions exhibits a 98% mutation ratio, immediately triggering a high-severity ransomware flag without interrupting legitimate backups. 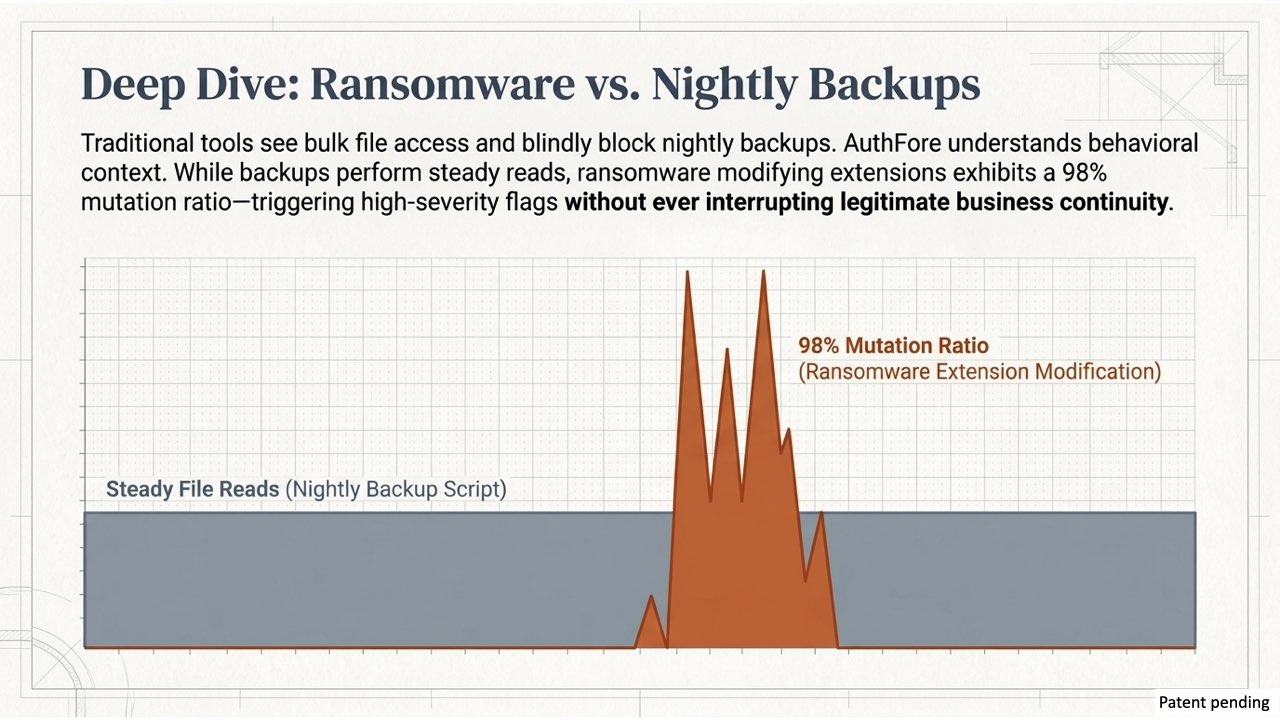 |
| Kerberoasting Attack Identification A malicious insider requesting TGS service tickets for 50 distinct SPNs within 10 seconds is flagged by the adreconciler as an active Kerberoasting campaign. 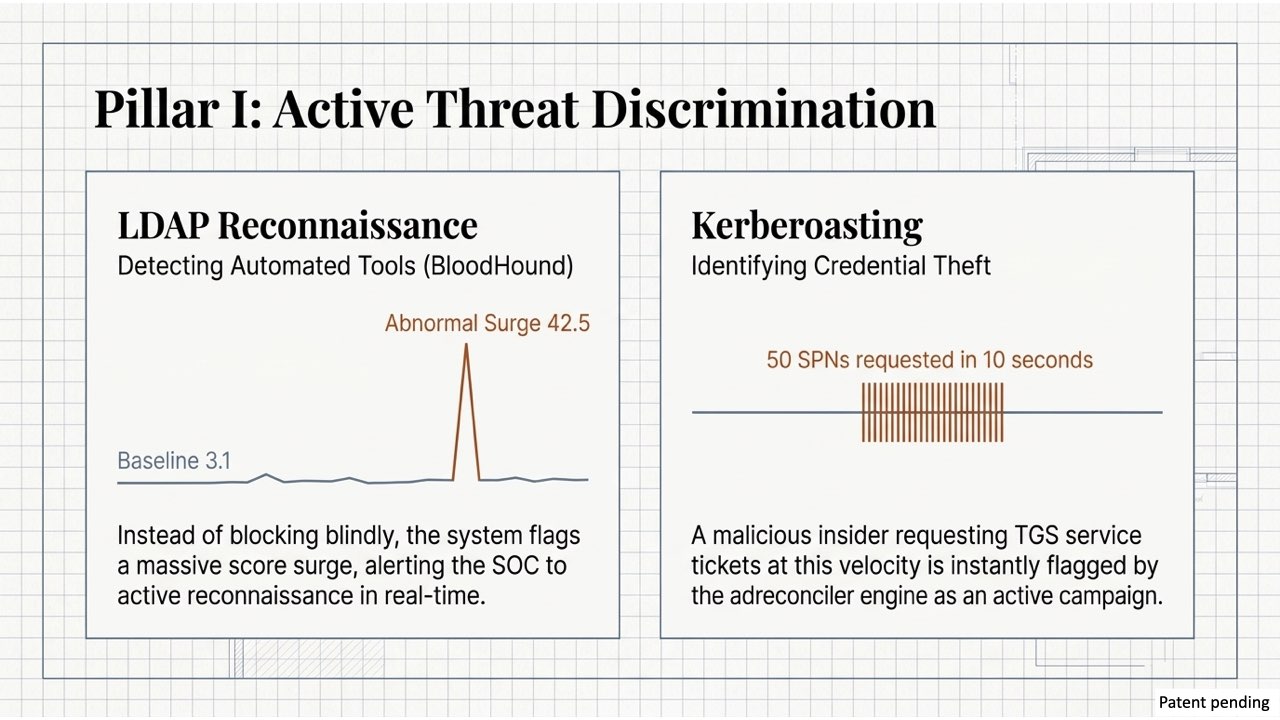 |
| Unusual Financial Data Extraction A payroll manager executes bulk SELECT queries outside business hours. dbmonitor detects the 15x spike in database touchpoint cost over baseline, flagging potential insider data theft. 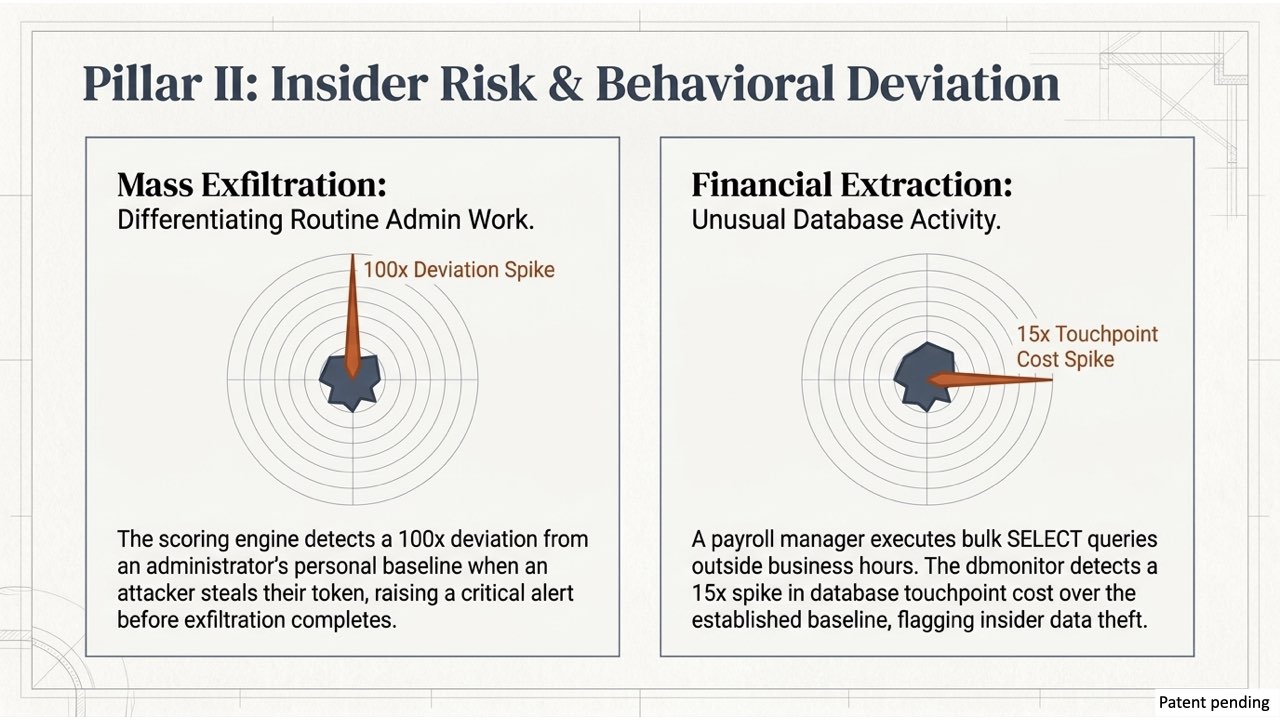 |
| Unified Multi-Protocol Activity Correlation The Canonical Resolver attributes all cross-protocol touchpoints (Kerberos, NFS, LDAP) to a single master identity, preventing split-identity evasion. 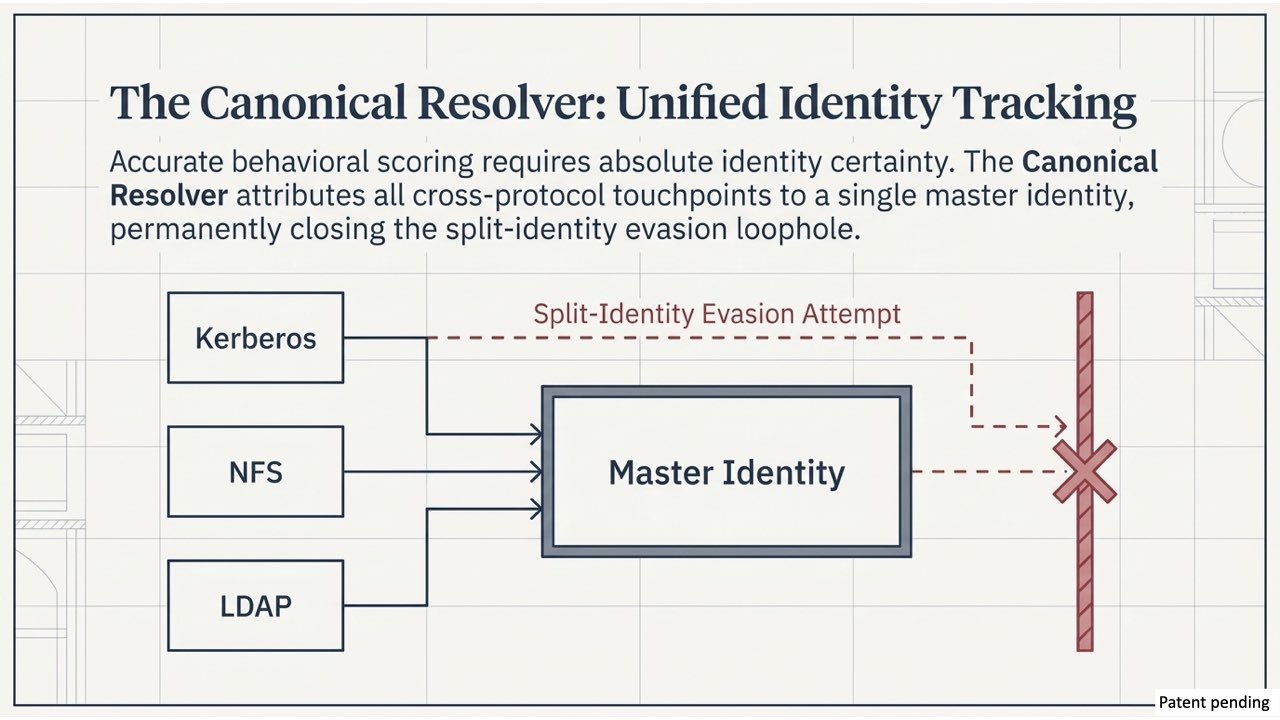 |
| Tamper-Evident Forensic Auditing A rogue IT admin attempts to erase log evidence. The hash-chain verification tool detects a broken hash link, proving data tampering to compliance auditors. 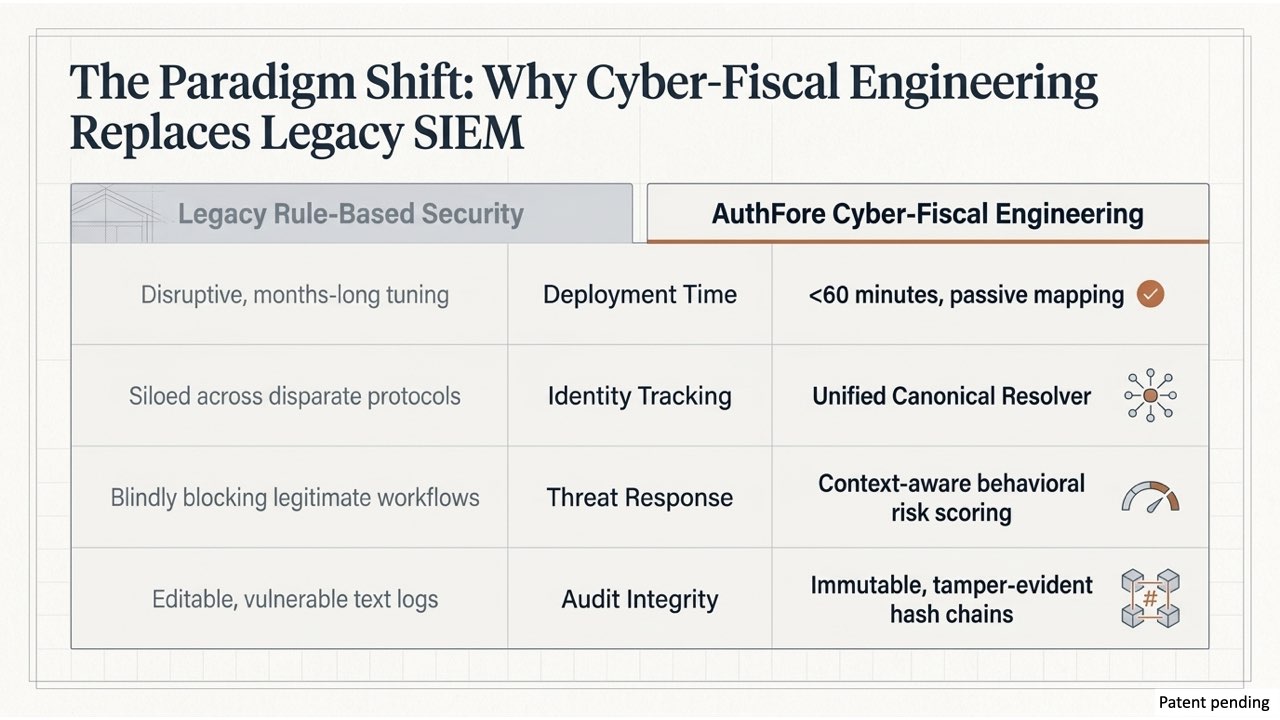 |
| Differentiating Routine Admin Work The scoring engine detects 100x deviation from an admin's personal baseline when an attacker steals their token for mass exfiltration, raising a critical alert. |
| Frictionless Onboarding (Zero False Positives) During the first 14 days, the system maps baseline burn rates for every department so normal operations cause zero false alarms when active monitoring opens. 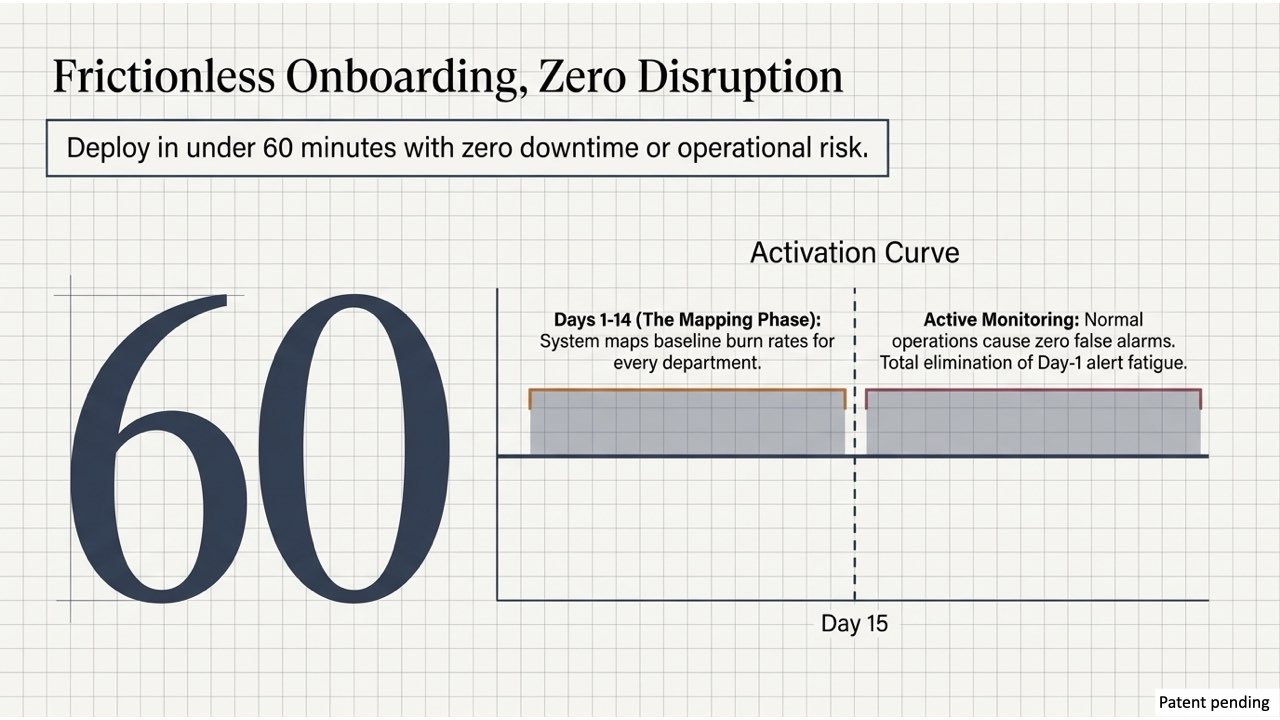 |
| Accurate AI Cost & Risk Attribution AuthFore's binder rule attributes database query costs directly to the human requester's budget, preventing users from using AI agents to bypass limits. 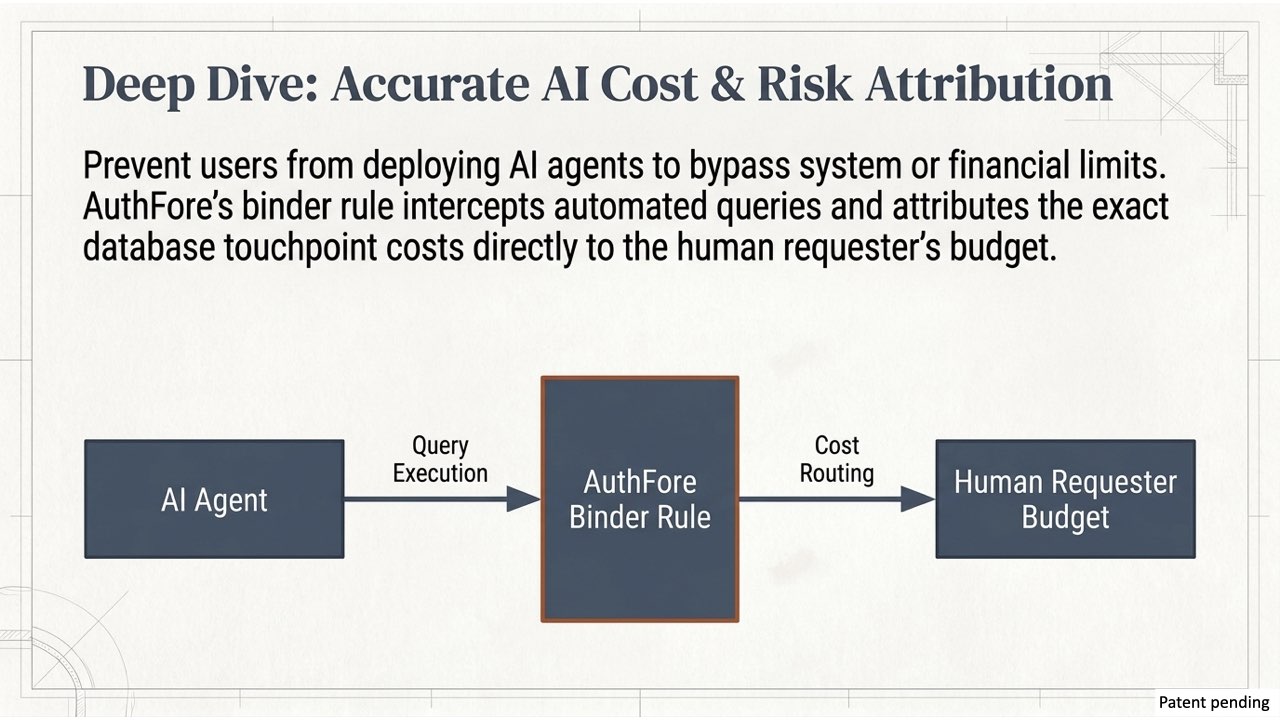 |
| EU AI Act & CCPA Compliance Forensics Provides an immutable, sequentially hashed ledger listing every query, data field accessed, and cryptographic signature for AI decisions. 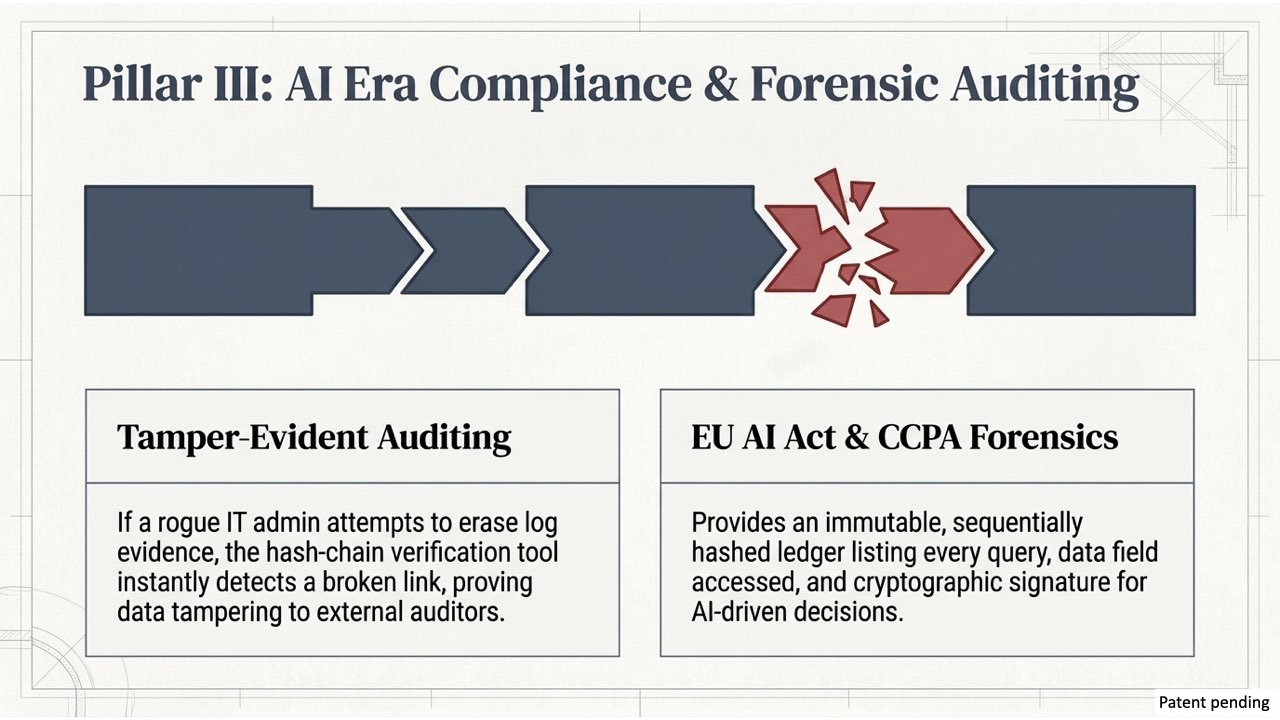 |
AuthFore Inc. - Dramatically Boosting CyberSecurity